Security & MFA
Protect your account with an authenticator app, and set your organization's sign-in policy. Your own two-factor setting is under Settings → Account. The organization policy is under Settings → Security.
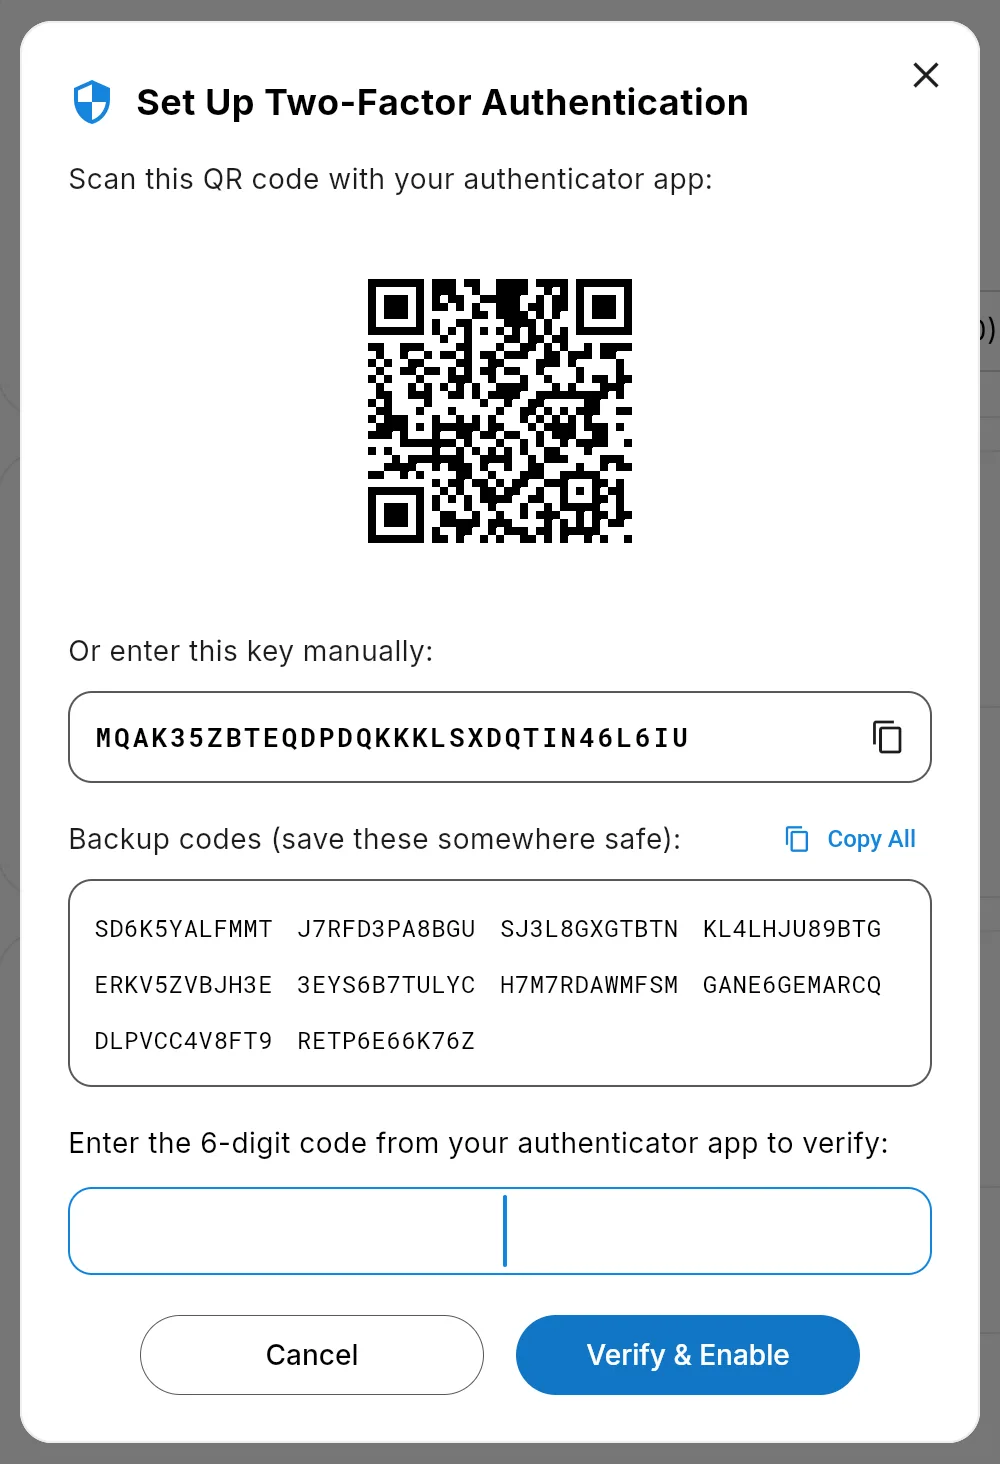
Turn on two-factor authentication
Flero uses authenticator apps (TOTP), such as 1Password, Authy or Google Authenticator. SMS codes are not offered.
- Open Settings → Account.
- Turn on the Two-Factor Authentication switch.
- Scan the QR code with your authenticator app, or enter the key shown under it by hand.
- Copy the backup codes with Copy All and store them somewhere safe. See Backup codes.
- Enter the 6-digit code from your app and click Verify & Enable.
From then on, every sign-in asks for a code after your password. You have 5 attempts before you must start the sign-in again. See Signing up and logging in.
To turn it off, switch Two-Factor Authentication off and confirm Disable 2FA. You cannot stay signed in without it if your organization requires it.
Backup codes
Flero shows 10 backup codes when you turn on two-factor authentication. Save them, but do not rely on them yet: the sign-in dialog does not currently accept them. If you lose access to your authenticator app, contact your administrator or Flero support.
When your organization requires 2FA
If an admin turns on Require Two-Factor Authentication, anyone without it is stopped at sign-in with "Two-Factor Authentication Required. Your organisation requires two-factor authentication. Please set up 2FA to continue." They follow the same steps as above, then click Verify & Enable 2FA to continue.
Sessions
Settings → Account → Active Sessions lists where you are signed in, with Revoke on each row. See Account.
Repeated failed sign-ins on one email are throttled. After too many attempts, sign-in answers "Too many attempts" for a while.
Organization security policy
Settings → Security is visible to organization members. Only organization admins can change it.
Authentication Policy
| Setting | Options |
|---|---|
| Require Two-Factor Authentication | On or off. When on, every user must set up 2FA to sign in. |
| Session Timeout | 1 hour, 4 hours, 8 hours, 24 hours or 7 days |
| Max Concurrent Sessions | 1, 3, 5, 10 or Unlimited |
Click Save Authentication Policy.
Password Policy
| Setting | Options |
|---|---|
| Minimum Password Length | 8, 10, 12, 14 or 16 |
| Require Uppercase Letters, Require Numbers, Require Special Characters | On or off |
| Max Password Age | 30, 60, 90 or 180 days, or Never |
| Password History | 3, 5, 10 or 15 |
Click Save Password Policy.
What is enforced today: Flero enforces Require Two-Factor Authentication at sign-in. The session and password values are saved with your organization but not yet applied. Every password must still be at least 8 characters and must not appear in known breaches.
Tips & gotchas
- Set up 2FA before you need it. Turning it on after an incident is too late.
- Add your authenticator to a second device or a password manager if your app supports it, so losing one phone does not lock you out.
- Warn people before you require 2FA. Everyone without it is asked to set it up on their next sign-in.
Related
Found something out of date? This page lives in the Flero docs content set.