Credential scope
Scope decides who can see and use a credential. There are three: Personal, Workspace and Organization. You choose it when you create the credential, and it cannot change afterwards.
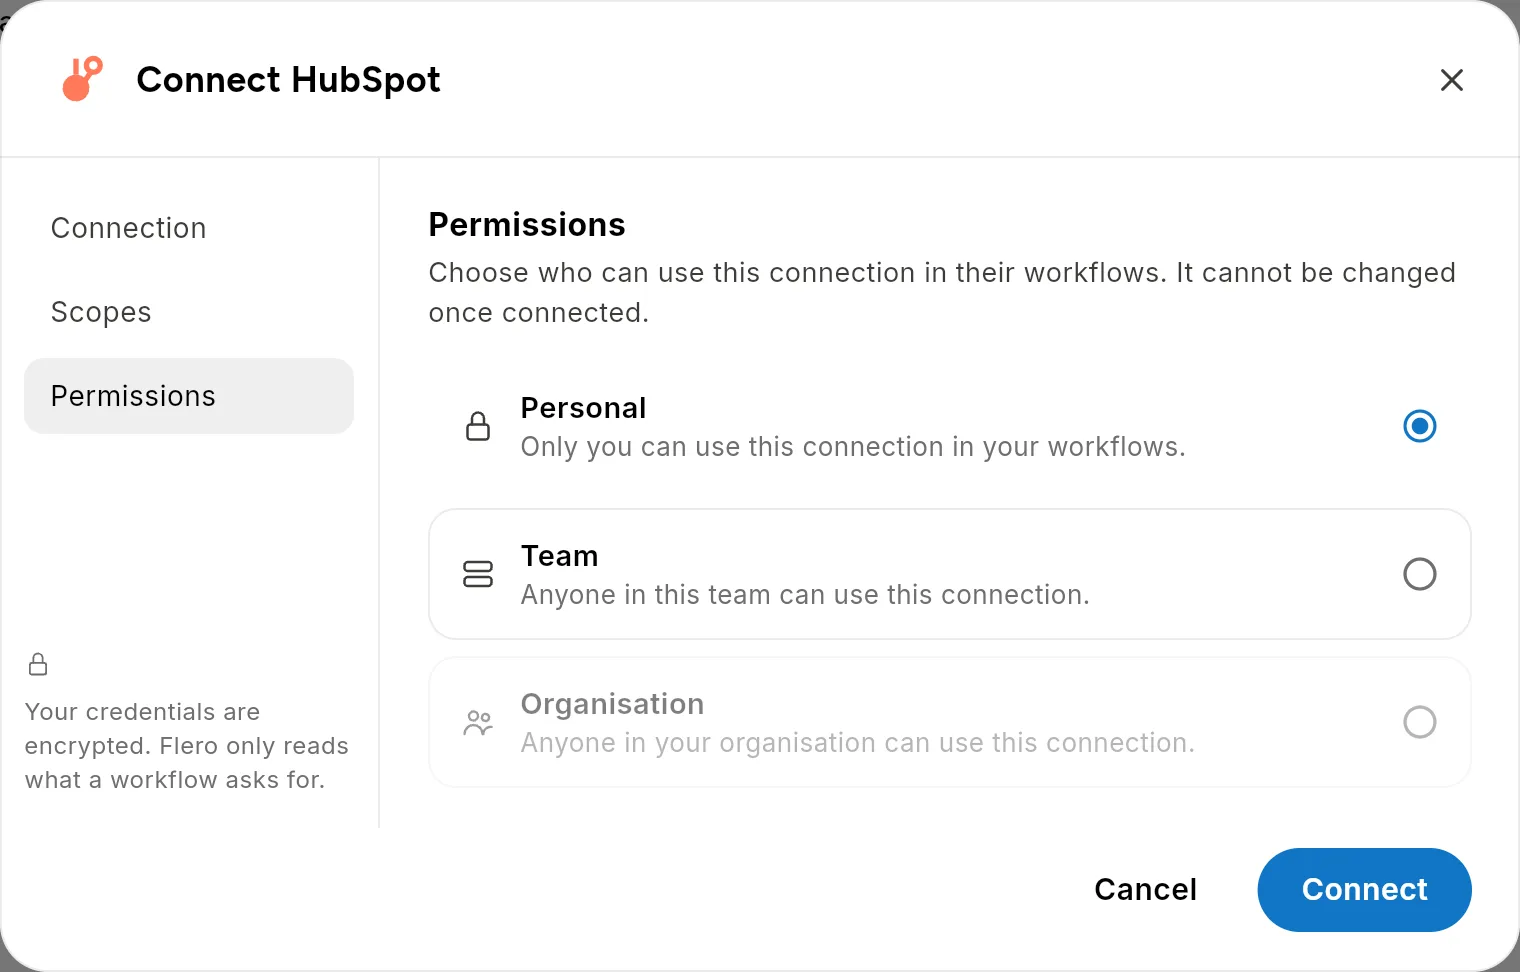
The three scopes
Personal
Only you can see, use, edit or delete it. This is the default.
Use it for:
- Your own accounts and tokens that nobody else should use.
- Trying something out without affecting teammates.
Workspace
Every member of this workspace can see it and pick it in their workflows. Workspace owners and admins can edit or delete it.
Use it for:
- Shared service accounts: the team's Slack app, the support mailbox, the company HubSpot portal.
- Anything two or more teammates need.
"Sign in with …" buttons in connector nodes create Workspace credentials. See OAuth flow.
Organization
Every organization member can see it and use it, across all the organization's workspaces. Organization owners and admins can edit or delete it.
Use it for:
- Resources every workspace needs, such as one production Salesforce org.
Someone added to a single workspace, without organization membership, does not see Organization credentials.
Who can create each scope
| Scope | Who can create it |
|---|---|
| Personal | Any signed-in user |
| Workspace | Workspace owners and admins, and organization admins |
| Organization | Organization owners and admins |
The credential dialog only offers the scopes you can create. If you see no Scope chips, you can create Personal credentials only.
Choosing a scope
| You're storing… | Scope |
|---|---|
| Your own token while you build | Personal |
| The team's Slack app or shared mailbox | Workspace |
| The company Salesforce org every team uses | Organization, or Workspace if only one workspace uses it |
If unsure, ask a workspace admin to create it at Workspace scope.
Changing scope
Scope is fixed once the credential exists. The Scope chips show a lock icon when you edit a credential.
To move a credential to another scope:
- Create a new credential at the scope you want.
- Point the workflows at the new credential.
- Delete the old one.
Tips & gotchas
- Organization credentials cross workspace boundaries. A workspace kept separate for compliance still sees them. Use Organization scope only for credentials every workspace may use.
- Hidden means not found. Opening a credential you cannot see returns "not found" rather than "forbidden", so its existence is not revealed.
- Flero API keys are not credentials. They belong to the user who created them. See API keys & bearer tokens.
Related
Found something out of date? This page lives in the Flero docs content set.