OAuth flow
For services that use OAuth 2.0, you create a credential by signing in to the service in a popup. Flero exchanges the sign-in for tokens on the server and stores them encrypted. The tokens never reach your browser.
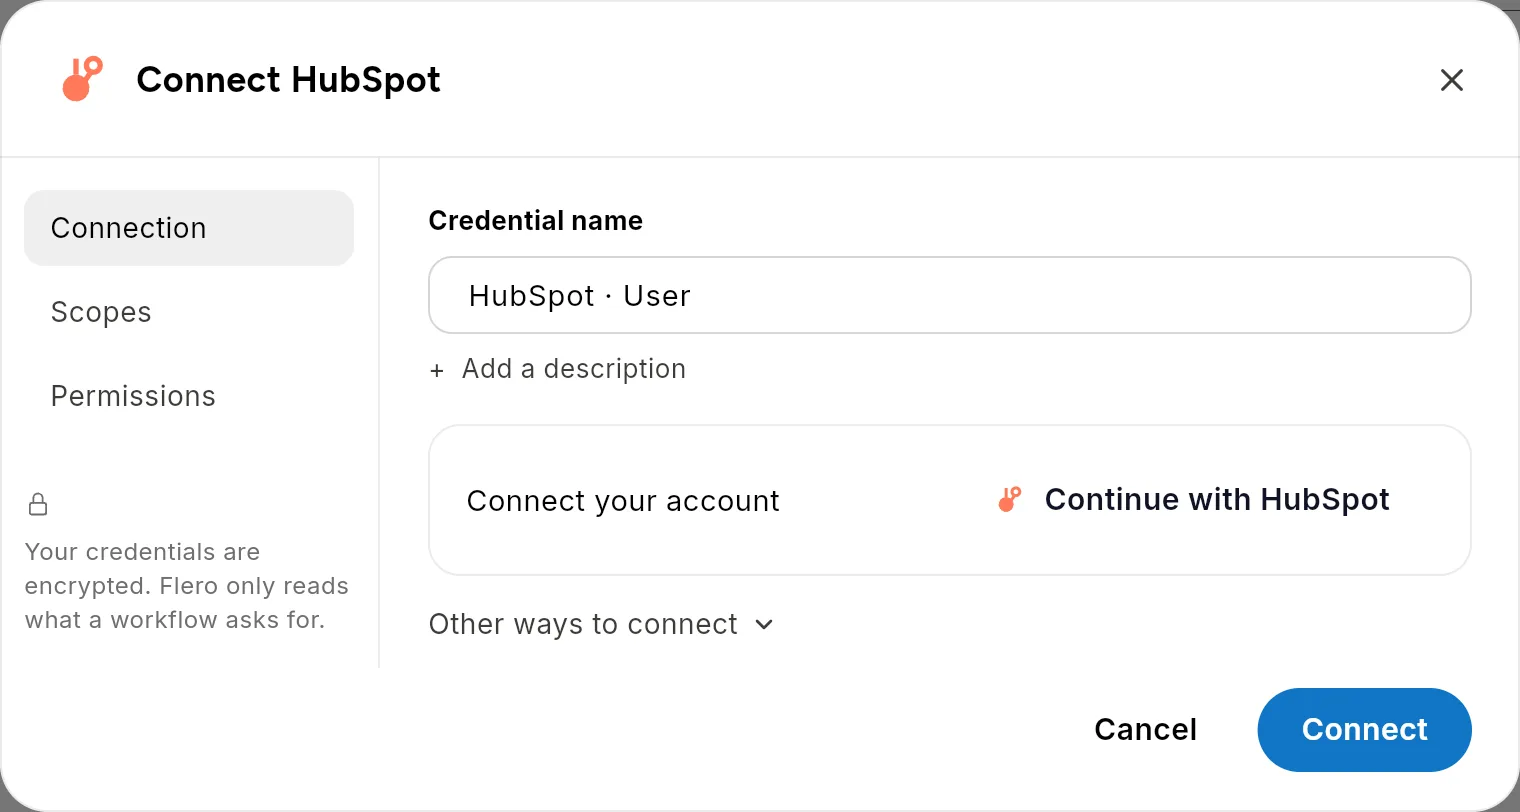
Two ways to connect
| Flero-managed sign-in | Your own app | |
|---|---|---|
| Where | Sign in with … button in a connector node | Add Credential in Settings → Credentials, or the node's credential picker |
| Setup | None. Flero owns the OAuth app. | Register an OAuth app with the service and paste its client ID and secret |
| Permissions | A fixed set, listed on each connector page | You choose from the scopes the connector supports |
| Credential scope | Workspace | Whatever you pick |
Flero-managed sign-in
Some connectors can use an OAuth app that Flero registered with the provider. Drop the connector node on the canvas and click Sign in with … above the credential picker.
| Provider | Connectors |
|---|---|
| Slack | Slack |
| HubSpot | HubSpot CRM |
| Microsoft | Outlook, Teams, SharePoint, OneDrive, OneNote, Excel |
| Salesforce | Salesforce CRM |
| Airtable | Airtable |
| Gmail, Google Calendar, Drive, Sheets, Google Cloud. The managed Google app is still in Google's review, so Sign in with Google is not yet offered in customer workspaces. Use your own Google app for now. |
What to expect:
- The sign-in creates a Workspace credential, so teammates can use it. The node shows "Signed in as
", the person who signed in. - The next time you add the same connector, Flero attaches your existing managed credential automatically.
- To use a different account, pick another credential from Change credential.
- Microsoft and Google share one app across their connectors. When you sign in to a second connector from the same provider, Flero offers to merge the sign-in into your existing credential ("Reuse an existing sign-in?"). Merging re-runs the consent with the combined permissions, so one credential serves both connectors.
Your own app
Use your own OAuth app when the connector has no managed app, when your security policy requires it, or when you need different permissions.
- In the service's developer console, register an OAuth app.
- In Flero, open Add Credential, pick the service, and choose OAuth 2.0.
- Copy the Redirect URL from the dialog into your app's allowed redirect URLs. On Flero's hosted service it is
https://oauth.flero.ai/callback. - Paste the app's Client ID and Client Secret.
- Fill in any service-specific fields, such as the Shopify shop name or the ServiceNow instance.
- Untick any scopes you do not need.
- Click Connect with ….
What happens during sign-in
- A popup opens on the service's sign-in page.
- Sign in if you are not already signed in.
- The service shows the permissions Flero asks for. Check the account shown at the top.
- Click Allow, or the service's equivalent.
- The popup shows a confirmation and closes itself about two seconds later.
- The dialog confirms the connection. The credential is saved.
The sign-in must finish within 10 minutes of clicking Connect. If the popup does not report back within 5 minutes, the dialog stops waiting. Start again.
Admin approval
Some services need an administrator before ordinary users can connect:
- Microsoft 365: some permissions need a tenant administrator's consent once for the whole organization. If you see "Need admin approval", ask your Microsoft 365 admin.
- HubSpot: the person connecting must be a super admin or have the App Marketplace Access permission in the HubSpot portal.
- Salesforce: the connected app must be installed or approved in your org. Flero's callback page explains the "app not installed" error when it occurs.
Keeping tokens fresh
Access tokens are short-lived. Flero refreshes them for you:
- In the background, every 5 minutes, for OAuth credentials that expire in the next 10 minutes.
- Before a node runs, when its token expires within a minute.
- Once, automatically, when a service rejects a call with
401.
If a refresh fails for good, for example because the user revoked access, the credential shows Reconnect required and nodes that use it fail. Edit the credential and click Reconnect. Workflows keep their reference to it.
Revoking access
- In Flero: delete the credential under Settings → Credentials.
- At the service: remove Flero from the account's connected apps. This is what actually invalidates the tokens. Do both if a credential may have leaked.
Troubleshooting
| Symptom | Cause |
|---|---|
| The popup does not open | A popup blocker. Allow popups for your Flero address and try again. |
redirect_uri_mismatch |
Your own app does not list the Redirect URL shown in the dialog. Add it exactly. |
invalid_client |
The client ID or secret is wrong, or belongs to another app. |
| "Invalid or expired OAuth state parameter" | More than 10 minutes passed, or two sign-ins ran at once. Start again. |
| The consent screen shows the wrong account | You are signed in to the service with another account in this browser. Sign out there, then retry. |
Calls fail with 403 after a successful sign-in |
The account or app lacks a permission the operation needs. Check the connector page, then reconnect with the right scopes. |
Related
- Managing credentials
- Connector catalog: per-service permissions
- Credential scope
Found something out of date? This page lives in the Flero docs content set.