Roles & permissions
Each workspace member has one of four roles: Owner, Admin, Editor or Viewer. Organizations add a second layer: organization members are either a User or an Admin. Roles are fixed sets of permissions. You cannot customise them.
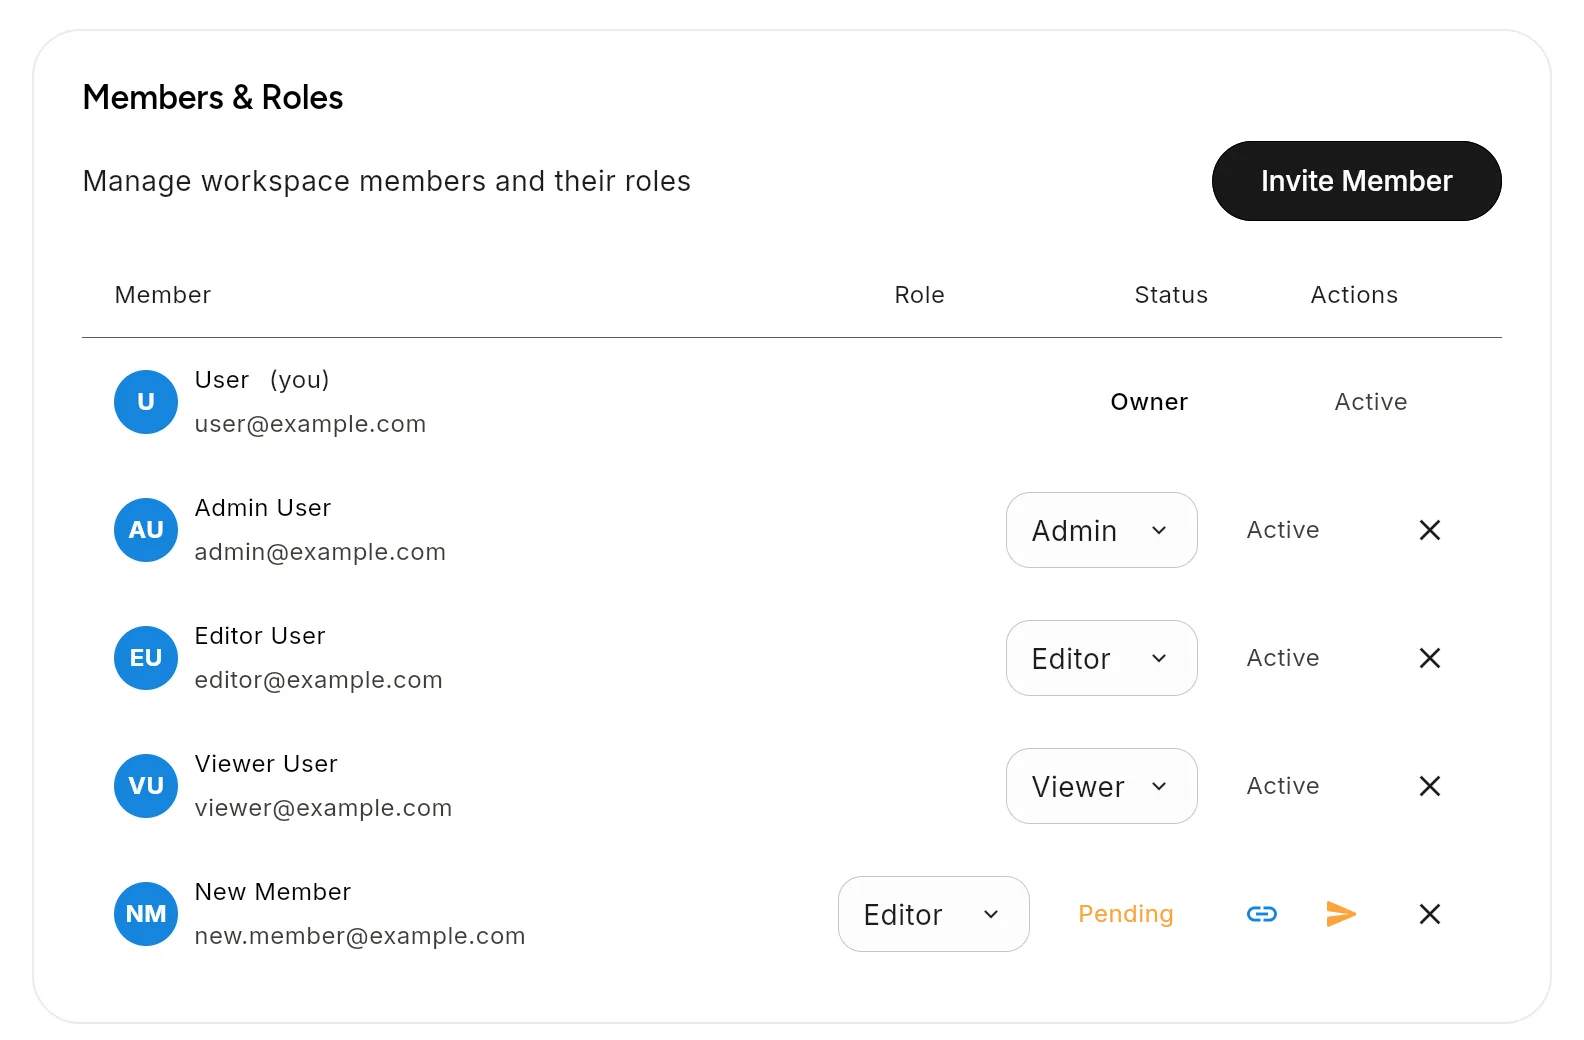
Workspace roles
| Role | Who has it | In short |
|---|---|---|
| Owner | The person who created the workspace. One per workspace. | Full control, including workspace settings and deletion |
| Admin | Granted by the owner or another admin | Manages members, variables, alert rules and workspace credentials |
| Editor | Granted by an owner or admin. The default for new invites. | Builds and runs workflows |
| Viewer | Granted by an owner or admin | Works with workflows like an editor today, but cannot add Knowledge documents |
Permission matrix
| Action | Viewer | Editor | Admin | Owner |
|---|---|---|---|---|
| Open, build, run and archive workflows | ✅ | ✅ | ✅ | ✅ |
| View executions and logs | ✅ | ✅ | ✅ | ✅ |
| Create and manage your own Personal credentials | ✅ | ✅ | ✅ | ✅ |
| Use Workspace credentials | ✅ | ✅ | ✅ | ✅ |
| Create, edit and delete Workspace credentials | ❌ | ❌ | ✅ | ✅ |
| Add Knowledge documents to the workspace | ❌ | ✅ | ✅ | ✅ |
| Invite members, change roles, remove members | ❌ | ❌ | ✅ | ✅ |
| Add, edit and delete workspace variables | ❌ | ❌ | ✅ | ✅ |
| Change Workspace Alert Rules | ❌ | ❌ | ✅ | ✅ |
| Save General, Settings, Policies & Quotas and AI Budgets | ❌ | ❌ | ❌ | ✅ |
| Delete the workspace | ❌ | ❌ | ❌ | ✅ |
Viewer is not read-only yet. Flero checks workspace membership for workflow actions, not the Editor or Viewer role. A viewer can edit and run workflows. Give the Viewer role to people you trust to work in the workspace, and keep sensitive work in a separate workspace.
The owner role cannot be transferred or granted from the members list.
Credentials by scope
| Scope | Who can create and manage it | Who can see and use it |
|---|---|---|
| Personal | Its creator only | Its creator |
| Workspace | Workspace owners and admins, and organization admins | Members of that workspace |
| Organization | Organization owners and admins | Organization members, in any workspace |
A credential's scope is set when you create it and cannot change later. See Credential scope.
Organization roles
Your organization has its own member list under Settings → Organization. Each organization member is a User or an Admin. The person who owns the organization has full control.
| Action | Not an org member | Org User | Org Admin or owner |
|---|---|---|---|
| See the Billing & Usage, Security, Data & Privacy and Organization tabs | ❌ | ✅ (read-only) | ✅ |
| See Organization credentials | ❌ | ✅ | ✅ |
| Create, edit and delete Organization credentials | ❌ | ❌ | ✅ |
| Edit organization identity and settings | ❌ | ❌ | ✅ |
| Invite and remove organization members | ❌ | ❌ | ✅ |
| Change security and retention policies | ❌ | ❌ | ✅ |
Organization roles do not grant workspace access. To work in a workspace, an organization admin still needs to be a member of it.
Someone added to a single workspace is not an organization member. They see only the Account, Workspace, Appearance, Notifications and Credentials tabs in Settings. If they open an organization tab by link, they see "You don't have access to organization settings".
Tips & gotchas
- One owner per workspace. Owners cannot be removed and their role cannot change. Plan who creates each workspace.
- Admins cannot save workspace settings. Name, description, quotas and AI budgets save only for the owner.
- Removing someone from their last workspace deactivates them, unless they are an organization member. See Inviting members.
- No guest role. For people outside your team, use public approval links or a public form.
Related
Found something out of date? This page lives in the Flero docs content set.